


The image factory. It builds hardened container images from source on Wolfi with melange and apko, holds them to a hard 0-CVE gate, signs them with cosign, and publishes to GHCR.
300+ hardened images for the infrastructure you actually run. No Dockerfiles. Nothing inherited from another distro. Free, signed, and rebuilt daily.
Part of QuenchWorks, the 0-CVE replacement for the Bitnami catalog. Browse every image, with versions and digests, at quench-works.com/images.
Every image in the catalog:
- is built from source, no Dockerfile, nothing carried over from another distro. Where an upstream is infeasible to compile in CI (ClickHouse, ScyllaDB, CockroachDB, Dragonfly, MongoDB), we ship the project's own official binary and harden the base around it,
- clears a hard 0 fixable CVE gate (Trivy, fail-on-fixable) before anything is published,
- runs as nonroot (uid 1001) on a read-only root filesystem,
- ships as a multi-arch index (linux/amd64 + linux/arm64), signed and pinned by digest,
- carries an SBOM and a cosign keyless signature.
The catalog spans databases, caches, search and vector, streaming, coordination, observability, gateways and proxies, object storage, secrets and identity, plus a container registry (Harbor), Git (Gitea), and CI/IaC (Atlantis).
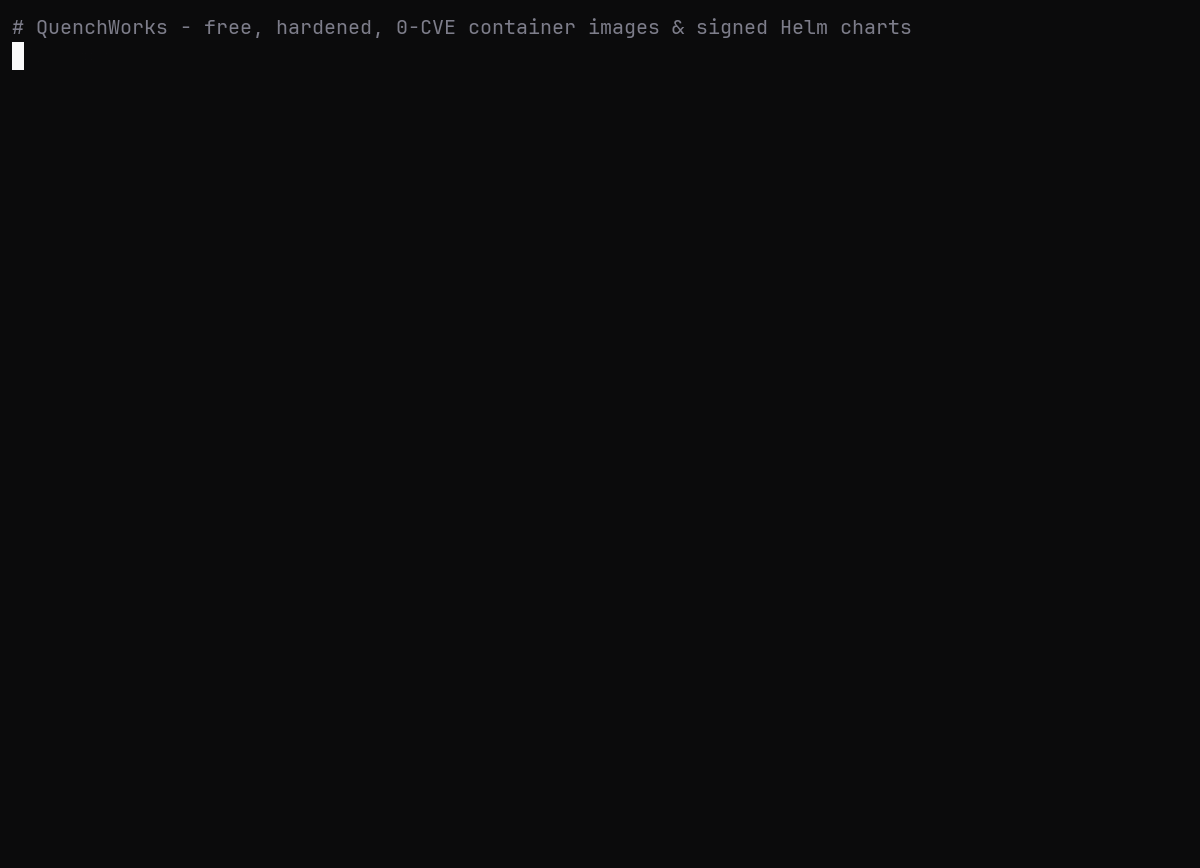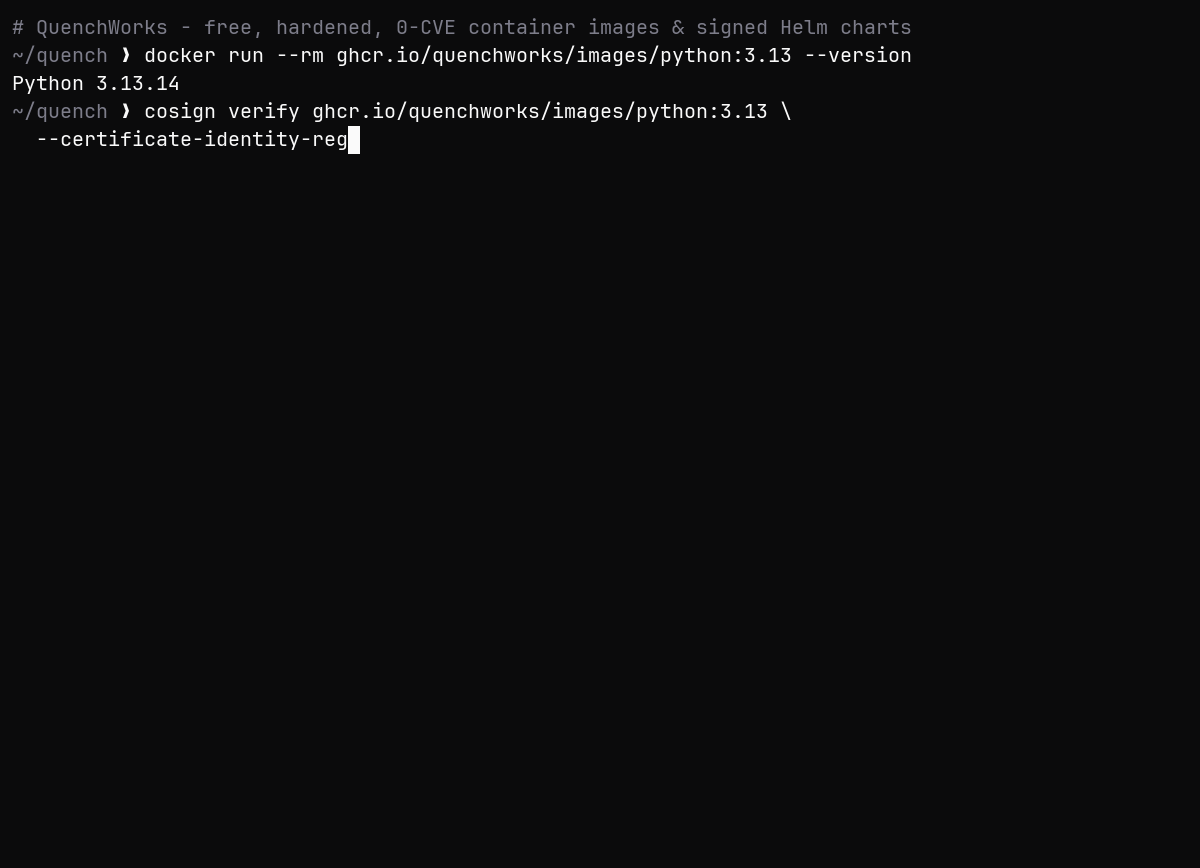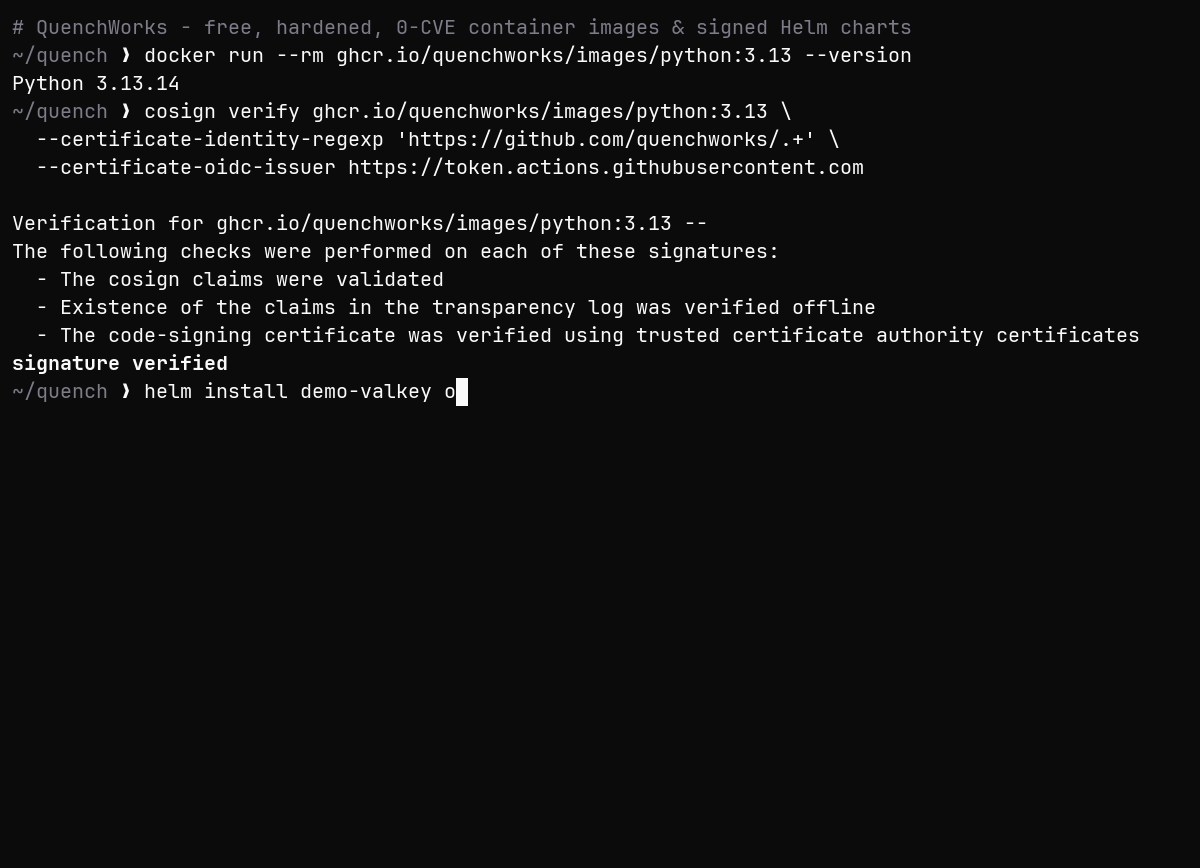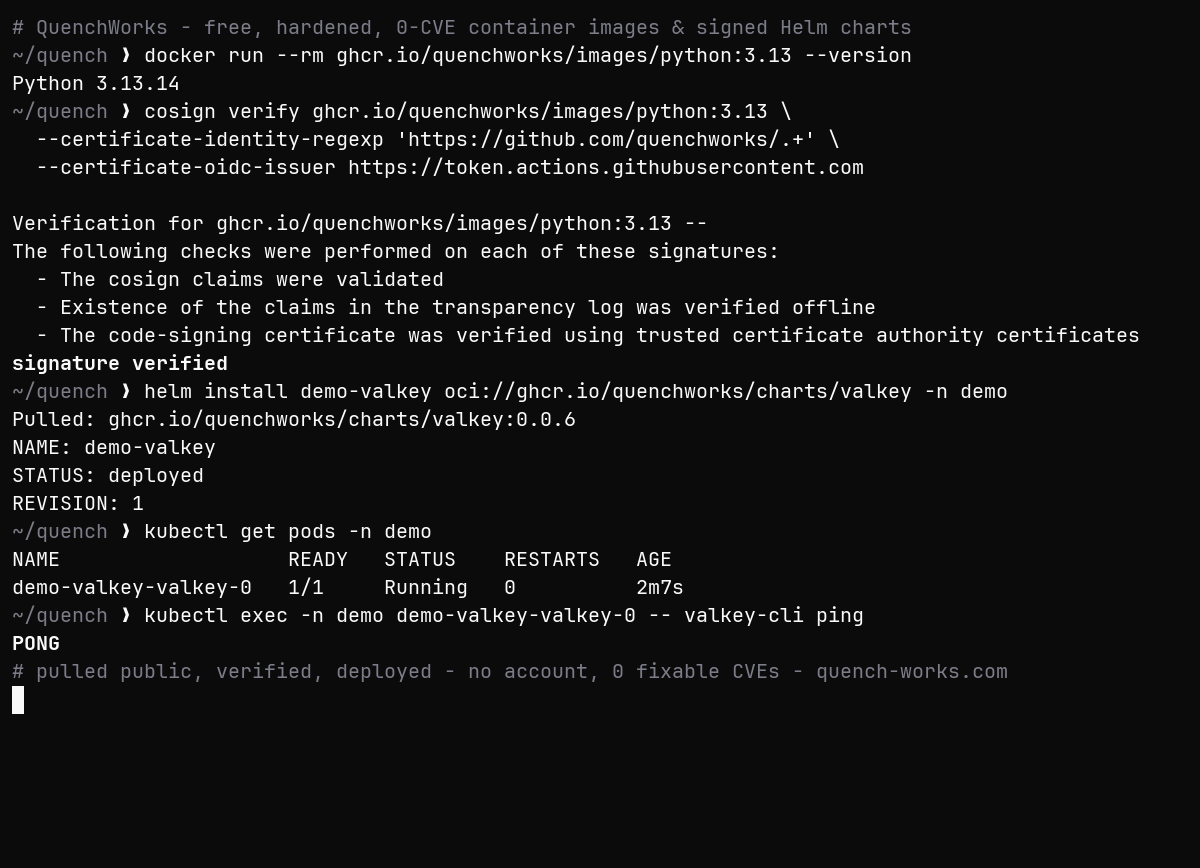
# images are tagged by version (there is no :latest); swap redis:8.8.0 for any image and version
docker pull ghcr.io/quenchworks/images/redis:8.8.0

cosign verify ghcr.io/quenchworks/images/redis:8.8.0 \
  --certificate-identity-regexp 'https://github.com/quenchworks/.+' \
--certificate-oidc-issuer https://token.actions.githubusercontent.com- melange compiles the app from source into a signed APK.
- apko assembles a minimal, nonroot, multi-arch image and writes it to a local tar.
- Trivy scans that tar with
--exit-code 1 --ignore-unfixed. A single fixable CVE fails the build, and nothing is published. - Only once the gate passes, apko publishes to
ghcr.io/quenchworks/images/<app>as a multi-arch index. - cosign signs the digest (keyless).
- A dispatch tells the charts repo to repin the matching chart to the new digest.
The build runs on every change and once a day. That daily rebuild is the point: a clean scan stays true tomorrow instead of quietly aging out.
catalog.yaml                 source of truth: app, version, source, license, tier, status
apps/<app>/melange.yaml      build the package from source
apps/<app>/apko.yaml         assemble the minimal nonroot image
apps/<app>/test.sh           smoke test the built image
docs/                        build conventions
.github/workflows/           per-app build, scan, sign, dispatch
Go recipes that raise a dependency past a CVE must follow
docs/go-module-float.md — a bare go get mod@version
is silently defeated by an upstream replace, and silently inverts into a
downgrade once upstream moves past the pin.
Add a row to catalog.yaml, then create apps/<app>/ with a melange build, an apko config, and a test. Charts are authored separately in the charts repo, from each app's own upstream docs. See CONTRIBUTING.
Most of the catalog is OSI-clean. Four datastores are source-available and carried with a loud license note in catalog.yaml and on the website, because they are not OSI-approved open source: MongoDB and Elasticsearch (SSPL-1.0), CockroachDB and Dragonfly (BUSL-1.1). Each names the clean alternative we recommend instead: Valkey, OpenSearch, FerretDB + DocumentDB.
MIT for this repository's build configs and tooling. Each built image carries its upstream software's own license, recorded in catalog.yaml and the image labels.